
Terraforming the blast radius: Building secure, scalable cloud foundations with policy and automation
Modular infrastructure as code, policy guardrails and approval-gated pipelines shrink the blast radius of cloud mistakes before the first workload ever lands.

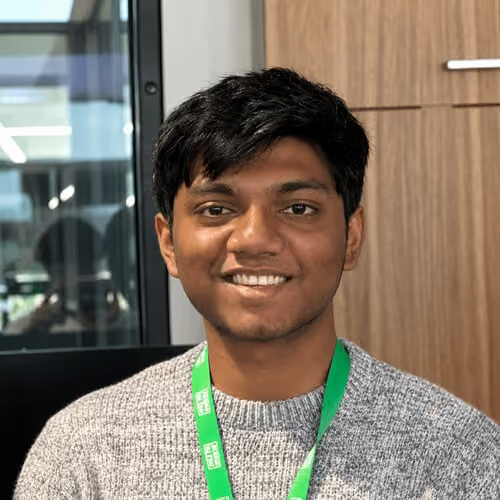
Session Details
Cloud platforms are excellent at helping teams move fast. They are also excellent at turning one rushed decision into a surprisingly large crater. This talk is about making the crater smaller. Because “we’ll lock it down later” is not a cloud strategy.
Drawing on real cloud and platform security work, plus a secure cloud baseline lab built with Terraform, policy, and pipelines, this session shows how to build foundations that reduce blast radius before the first workload lands. Rather than starting with a giant landing-zone diagram or a shopping list of controls, the talk focuses on design choices that matter in practice: modular infrastructure as code, environment separation, remote state hygiene, identity and privilege boundaries, policy guardrails, approval-gated delivery, and exception handling that does not turn into permanent chaos.
The session walks through a practical pattern for creating secure, scalable cloud foundations using Terraform modules, policy as code, and automation in CI/CD. It covers how to structure reusable modules without hiding risk behind abstraction, how to combine preventative and detective controls, how to keep repository and deployment workflows trustworthy, and how to use reviews, required checks, and approvals without making engineering teams hate the platform. It also explores common failure modes: over-privileged service connections, policy sprawl, state mismanagement, environment drift, “temporary” exceptions that never leave, and compliance evidence that only appears when an auditor is already asking questions.
Examples will draw on Azure-based baseline work, but the patterns are transferable across cloud platforms and delivery stacks. This is not a product pitch, and it is not a promise that automation will magically fix ownership, culture, or bad architecture. It is a grounded look at how policy and automation can make secure delivery the default, make risky changes harder to ship accidentally, and make the inevitable mistakes smaller, slower, and easier to recover from.
Attendees will leave with a concrete mental model for “terraforming the blast radius”: shaping the underlying platform so that misconfiguration, privilege creep, and rushed delivery have less room to become incidents. The goal is not perfect cloud security. The goal is secure enough by default, scalable under pressure, and boring in the best possible way. This session is aimed at cloud architects, platform engineers, security practitioners, and technical leaders who want stronger foundations without killing delivery speed.
There's More Where This Came From
Browse hundreds of sessions and build an agenda around the topics that matter to you.







