Main Program
14-16 October 2026 | Melbourne Convention & Exhibition Centre
Browse the program and start planning your CyberCon 2026 experience across three days of keynotes, panels, workshops, and more.
Results 1
Showing1 to 3 of 6
Build your own potato - an exploration of how Windows authentication abuse "actually works"

Building a Potato exploit from scratch explains why these privilege escalation techniques keep working despite years of Microsoft patching.
Privileged by design: The attack paths you already built


MFA and EDR alone cannot stop attackers who exploit administrative practices and identity workflows, the attack paths organisations already built themselves.
Global cyber security board reporting research results are in. How to ensure your reporting makes the grade?

New research across 67 boards reveals why most directors rate cyber security reporting poorly, and introduces a framework to align expectations.
Anatomy of hacktivist attacks: Detecting and mitigating emerging threats
A honeypot breach by a pro-Russian hacktivist group reveals current tactics against OT networks and the hardened controls that stop them.
After the incident burns: What the board didn't know, couldn't decide, and wished they'd asked

Seven real breaches reveal how governance failures, not technology gaps, determine whether an organisation recovers cleanly or falls apart.
From prompt injection to policy: Building a practical AI control framework for RAG, Copilots and Agents
A case study shows how one enterprise consolidated fragmented AI guidance into a governable control framework covering RAG, copilots and agentic systems.
Cyber resilience as critical infrastructure: Protecting Victoria's essential services
A Think Tank on cyber security as part of operational resilience for transport, health, water and utilities, and on lessons from regulated industries.
Ask me about leadership, governance and accountability
Thursday afternoon at 3.50pm, Ask an Expert 1 turns to leadership, governance and accountability with Theo Nassiokas of Wesfarmers Limited.
From chaos to calm: Making your organisation cyber resilient by designing and executing a CME from scratch
Building and running a crisis management exercise from scratch gives participants a repeatable model they can take back to their own organisation.
Taming the firehose: A spooling architecture for large MCP tool responses
An open-source spooling architecture stores large MCP tool responses outside the context window, returning only the summary an LLM actually needs to work with.
SANS Institute Workshop - Hands-on Agentic AI for digital forensics and incident response
A hands-on SANS FOR508 workshop: direct an agentic AI through a simulated DFIR investigation, then approve or reject each finding before it enters the case.
The science of recoverability: Why most organisations can't answer the one question that matters
The board wants to know how long until we are operational again, and the session's answer is that standard security metrics do not predict it.
Featured speaker with Tané Hunter
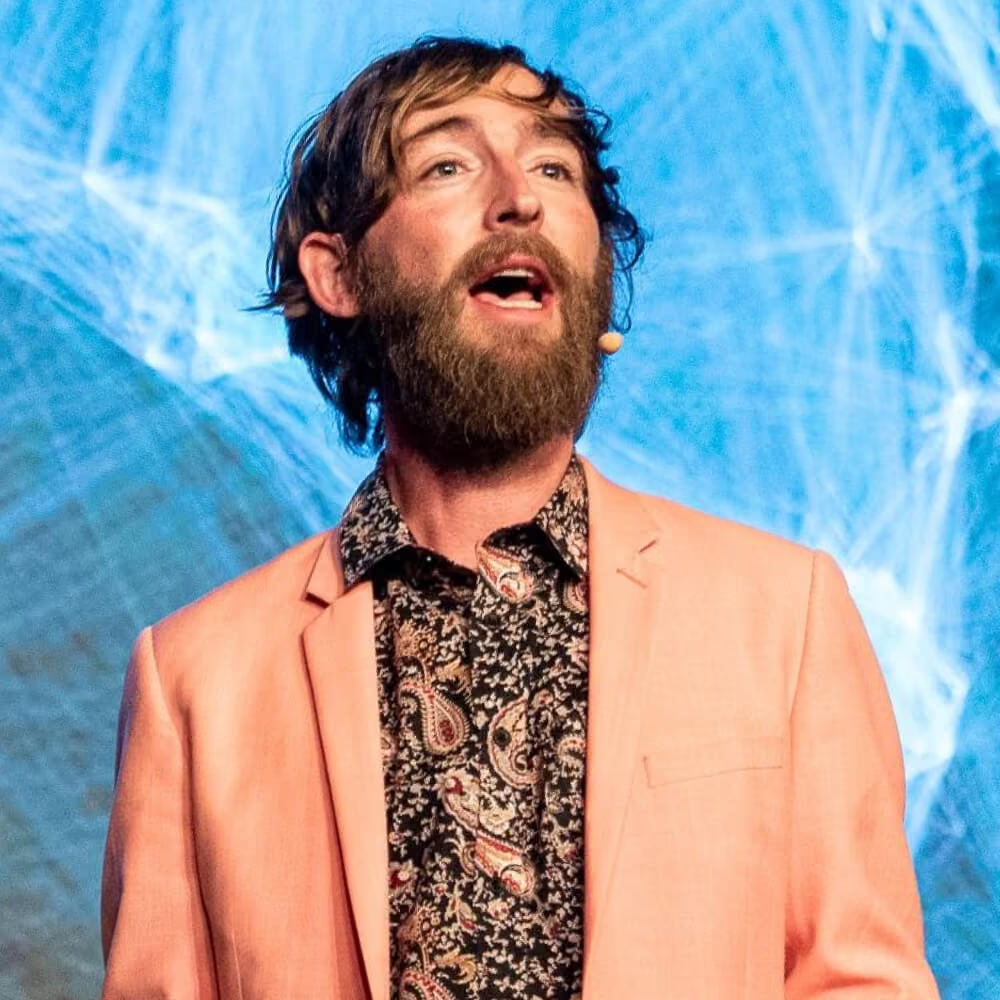
Tane Hunter built machine learning models at Australian research hospitals and wrote Full Stack Human. He has given over 500 keynotes across five continents.
Decoding cyber security: Growing an inclusive workforce
A panel on the new Cyber5050 report: what the survey data says about cyber's skills shortage and the barriers limiting women's participation and progression.
Trusted identity, autonomous agents: The new cybercrime battleground
Attackers now go after the accounts an organisation relies on and AI systems acting on its behalf, and this session shows how layered defence has to change.
Why I didn't hire you: 300+ hires, and what AI changed
Rezza Moeini draws on more than 300 hiring decisions to explain where candidates lose him, and why he now hires for judgement as entry-level work is automated.
From prompt to payment - securing agentic commerce
As AI agents start shopping and paying on people's behalf, this session maps the new commerce protocols and controls needed to secure transactions.
Securing the multi-cloud control plane in the age of AI agents
As AI agents gain power to manage cloud infrastructure, Tier 0 must expand beyond domain controllers to cover identity platforms and agentic access.
Still clicking: Why a billion-dollar industry hasn't moved the dial, and what actually has to change
A randomised trial found mandatory phishing training makes employees more likely to click, and this session explains why the model is broken and what works.
Different background, shared challenges: Women's experiences across GRC and security operations
Perspectives from governance, risk and security operations show how credibility is built, challenged and unevenly recognised for women in cyber security.
The next insider threat is already inside: How generative AI quietly accumulates power across the organisation
Generative AI embedded across enterprise tools quietly accumulates permissions and authority, and this session proposes governing it as a non-human insider.
Letting the cat out of the box, quantum sovereignty and future advantage
Q-Day will break RSA and ECC, and adversaries are already harvesting encrypted data to decrypt later. What building a sovereign quantum capability would take.
Your AI threat intelligence is broken. Here is what works
Most AI threat intelligence tools produce impressive but unusable summaries, and this session shows how to build systems that produce structured intelligence.
You reported the scams. They came back stronger: Why the Australian scams prevention framework needs a cyber intelligence mindset
Australians lost $2.18 billion to scams in 2025. How to read the Scams Prevention Framework as an operational blueprint that turns reporting into disruption.
Secure your place at CyberCon 2026
Join thousands of cyber security professionals in Melbourne this October.