Main Program
14-16 October 2026 | Melbourne Convention & Exhibition Centre
Browse the program and start planning your CyberCon 2026 experience across three days of keynotes, panels, workshops, and more.
Results 1
Showing1 to 3 of 6
Everybody saw the scams. Nobody owned them: Why fake news investment campaigns still slip past brands, platforms and enforcement
Fake news investment scams expose an ownership failure hiding inside a technical problem, and this session shows how brands and regulators can close it.
Bad cyber crisis decisions: An incident responder’s greatest hits and how to avoid repeating them

Anonymised DFIR case studies show how delayed escalation and misaligned executive priorities routinely turn a manageable incident into a worse one.
Are we secure? Empowering the enterprise through continuous, validated defense

A framework combining continuous security testing with adversary-based risk validation closes the gap between compliant on paper and secure in practice.
It’s essential, essentially: Strengthening cyber security guidance for operational technology
The Australian Government is writing its first cyber security framework for operational technology. Hear how OT Essentials is being built and where it stands.
Outgunned but not outmanoeuvred: How SMEs win the cyber war

Australian SMEs face relentless cybercrime with stretched IT teams, and practical, budget-fit steps can still close the gap adversaries exploit.
The referee's playbook: Converting 2025's privacy case law into your 2026 security budget

Two landmark 2025 OAIC privacy rulings set a legal baseline for reasonable security controls, giving CISOs court-tested language to justify next year's budget.
How to steal credentials and bypass MFA 2.0 (yes, it got worse)

Commodity phishing kits and infostealer economics have made MFA bypass routine, and this session sets out a tiered defence built from a real breach.
What happens if we’re wrong? Scenario analysis and the future of cyber security services

Scenario analysis stress-tests four cyber security service models against AI, geopolitical and social shifts to prepare for an unpredictable future.
AI compliance basics: Moving from policy to real-world implementation
A practical walkthrough of operationalising ISO 42001 and ISO 42005 AI impact assessments inside existing governance frameworks like ISO 27001.
Hunting the OT adversary: A behaviour-led operating model (constrain, observe, pursue)
A behaviour-led model built on constrain, observe, and pursue helps OT and ICS teams detect adversary movement before signature-based alerts fire.
Ask me about leadership, governance and accountability
Bring your leadership, governance and accountability questions to Dan Maslin at Ask an Expert 1 from 3.50pm on Wednesday 14 October.
The elephant in the SOC: Why no one sees identity whole
Starting from attackers who simply log in, the argument is that siloed teams and tools each see part of identity and privilege, and should work together.
Confessions of a Friendly Hacker: Why Attacker Thinking Is Our Best Defense in the AI Era
Known as the Friendly Hacker, Keren Elazari founded BSidesTLV and Leading Cyber Ladies, and researches security tech at Tel Aviv University.
Welcome Reception
Movie Night | "Midnight in the War Room" & "WarGames"
Awards Dinner
Exhibition Open and Arrival Coffee
Conference Opening
Keynote with Geoff White
Geoff White has delivered more than 300 keynotes. His investigations range from North Korea's hacking campaign to tech's transformation of money laundering.
Morning Tea
Featured speaker with Taher Elgamal
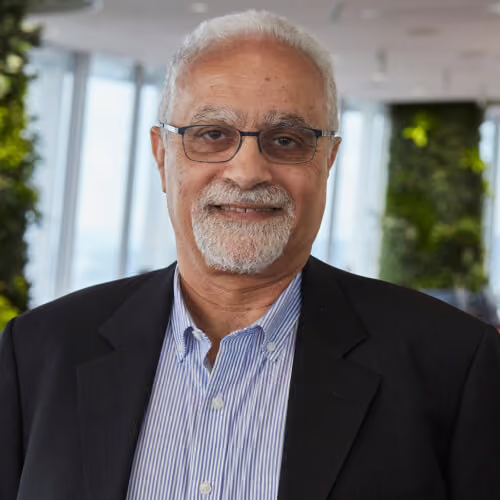
Taher Elgamal, a cryptographer recognised in the industry as the father of SSL, invented data security and digital signature standards for areas including DSS.
Aligning cyber intelligence with Australia's national resilience


Following the Slay Review, a panel debates whether mandatory threat sharing can turn critical infrastructure defence into a legislated sovereign capability.
Not if, but when: The Cyber Civilian Reserve - from concept to capability


Australia's newly established Cyber Civilian Reserve turns years of policy discussion into a deployable, industry-led national cyber capability.
When agentic AI works around your security controls
Whoever launches an agentic tool lends it their privileges, and the governance response covers scoping those permissions and monitoring what agents do.
Secure your place at CyberCon 2026
Join thousands of cyber security professionals in Melbourne this October.