Main Program
14-16 October 2026 | Melbourne Convention & Exhibition Centre
Browse the program and start planning your CyberCon 2026 experience across three days of keynotes, panels, workshops, and more.
Results 1
Showing1 to 3 of 6
Machine-speed adversaries, pragmatic defense
Manual triage buckles once attack paths are automated and non-deterministic, and a four-pillar operating model for AI threat readiness is offered instead.
Featured speaker with Kath Koschel
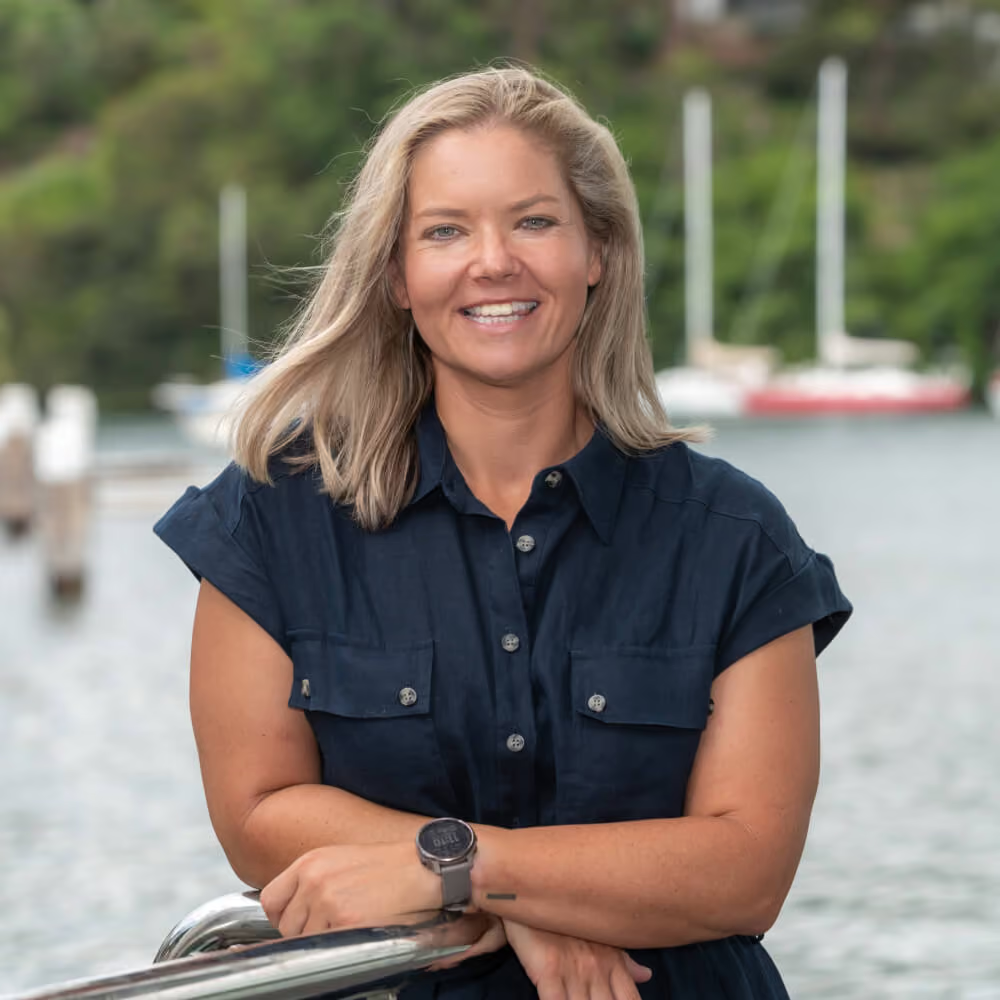
A former professional cricketer told she would never walk again, Kath Koschel taught herself to walk three times and founded The Kindness Factory.
Response reality: Lessons from cyber incidents
Incident response and cyber insurance practitioners unpack why outcomes depend less on having a response plan than on executing it under real pressure.
Security in the AI era: Cybersecurity through the eyes of the attacker & defender
Threat actors have moved from early monetisation schemes to AI-driven operations, and the response side has to modernise to keep pace.
The human layer in cyber security: what organisational culture does to your security posture
Research with Australian cyber professionals finds people in healthier cultures report near misses more readily. Leave with questions for your next interviewer.
AI on Kubernetes is a hidden attack surface
Hands-on findings on GPU container escapes, model-weight side channels, and agent trust failures that traditional cloud native tooling misses entirely.
The digital detective: How an internal OSINT challenge sparked organisation-wide engagement

An internal OSINT challenge covering 94 tasks showed staff across a power network how everyday online activity can expose far more than they realise.
From outreach to early career: What works in building sustainable cyber security pathways


National research across school outreach, university and workforce entry reveals a pathway continuity problem, not a talent shortage, and how to fix it.
Stopping the tank: Centre of gravity analysis for cyber threat prioritisation
Borrowed from military doctrine, centre of gravity analysis identifies the one dependency an attack would need to disrupt, making prioritisation defensible.
Cyber warfare: Uncomfortable truths about cyber munitions from the first quarter of the 21st century

From Stuxnet to NotPetya to a 2026 wiper attack on Stryker, this session tracks how state-built cyber weapons keep spilling over onto ordinary enterprises.
When code replaces blockades: Cyber attacks and the disruption of global trade


As Australian ports automate, cyber operations can create virtual chokepoints that disrupt trade flows, turning digital systems into national security risks.
The zero budget SOC. Using git, markdown and plain text to stop overthinking playbooks

Storing SOC playbooks as version-controlled markdown in git preserves institutional knowledge and keeps procedures maintainable without buying another platform.
Engineering our way out of tool fatigue, together

GRC engineering applies automation and systems thinking to cut through tool sprawl, building workflows that continuously validate real security risk.
One mistake away: The ransomware threat facing Australian organisations

Real ransomware engagements show attackers are typically inside for weeks before systems lock up, and by then the data is already gone.
From fake logins to live hijacking: How phishing targeting LastPass customers has evolved


Threat intelligence findings trace how one phishing campaign evolved from simple lures to real-time credential and session token harvesting using AI.
Hiding in plain sight: The shadow AI crisis nobody wants to own

Employees are feeding sensitive data into unauthorised AI tools daily, and this session argues Shadow AI is a governance failure needing practical controls.
Words are the new weapons

Simple natural-language prompts can bypass expensive AI security controls, and this session maps roughly 200 documented techniques for manipulating agents.
Browser extensions: Will you ever look at them the same again?
A working proof-of-concept extension with minimal declared permissions exfiltrates page content undetected, exposing weaknesses in store review trust.
Safety not guaranteed: What ransomware victims have in common with 1970s construction workers

Hundreds of ransomware incident responses show the same preventable causes each time, proving the failure is now governance, not technology.
Agentic AI at the edge: The security frontier worth owning

Autonomous AI agents are now running robotics and logistics systems without a human in the loop, and security architecture hasn't caught up.
40,000 CVEs and counting: What 60 years of AppSec tells us

Sixty years of AppSec history shows which vulnerability problems are structural, which are self-inflicted, and where security investment finally pays off.
Piracy-as-Infrastructure: Access, preservation, and resistance in a post-ownership world
As licensing replaces ownership across digital media, this session argues piracy has evolved into infrastructure for access and preservation.
The price of convenience: How surveillance capitalism turns your life into a product
An audit of Australia's top 50 websites found 74% at high privacy risk, showing how surveillance capitalism turns online behaviour into a tradeable asset.
Ask me about building secure technology and leadership, governance and accountability
Building secure technology and leadership, governance and accountability sit with ERQI co-founder Sriram Raghavan at 11.45am Thursday in Ask an Expert 1.
Secure your place at CyberCon 2026
Join thousands of cyber security professionals in Melbourne this October.